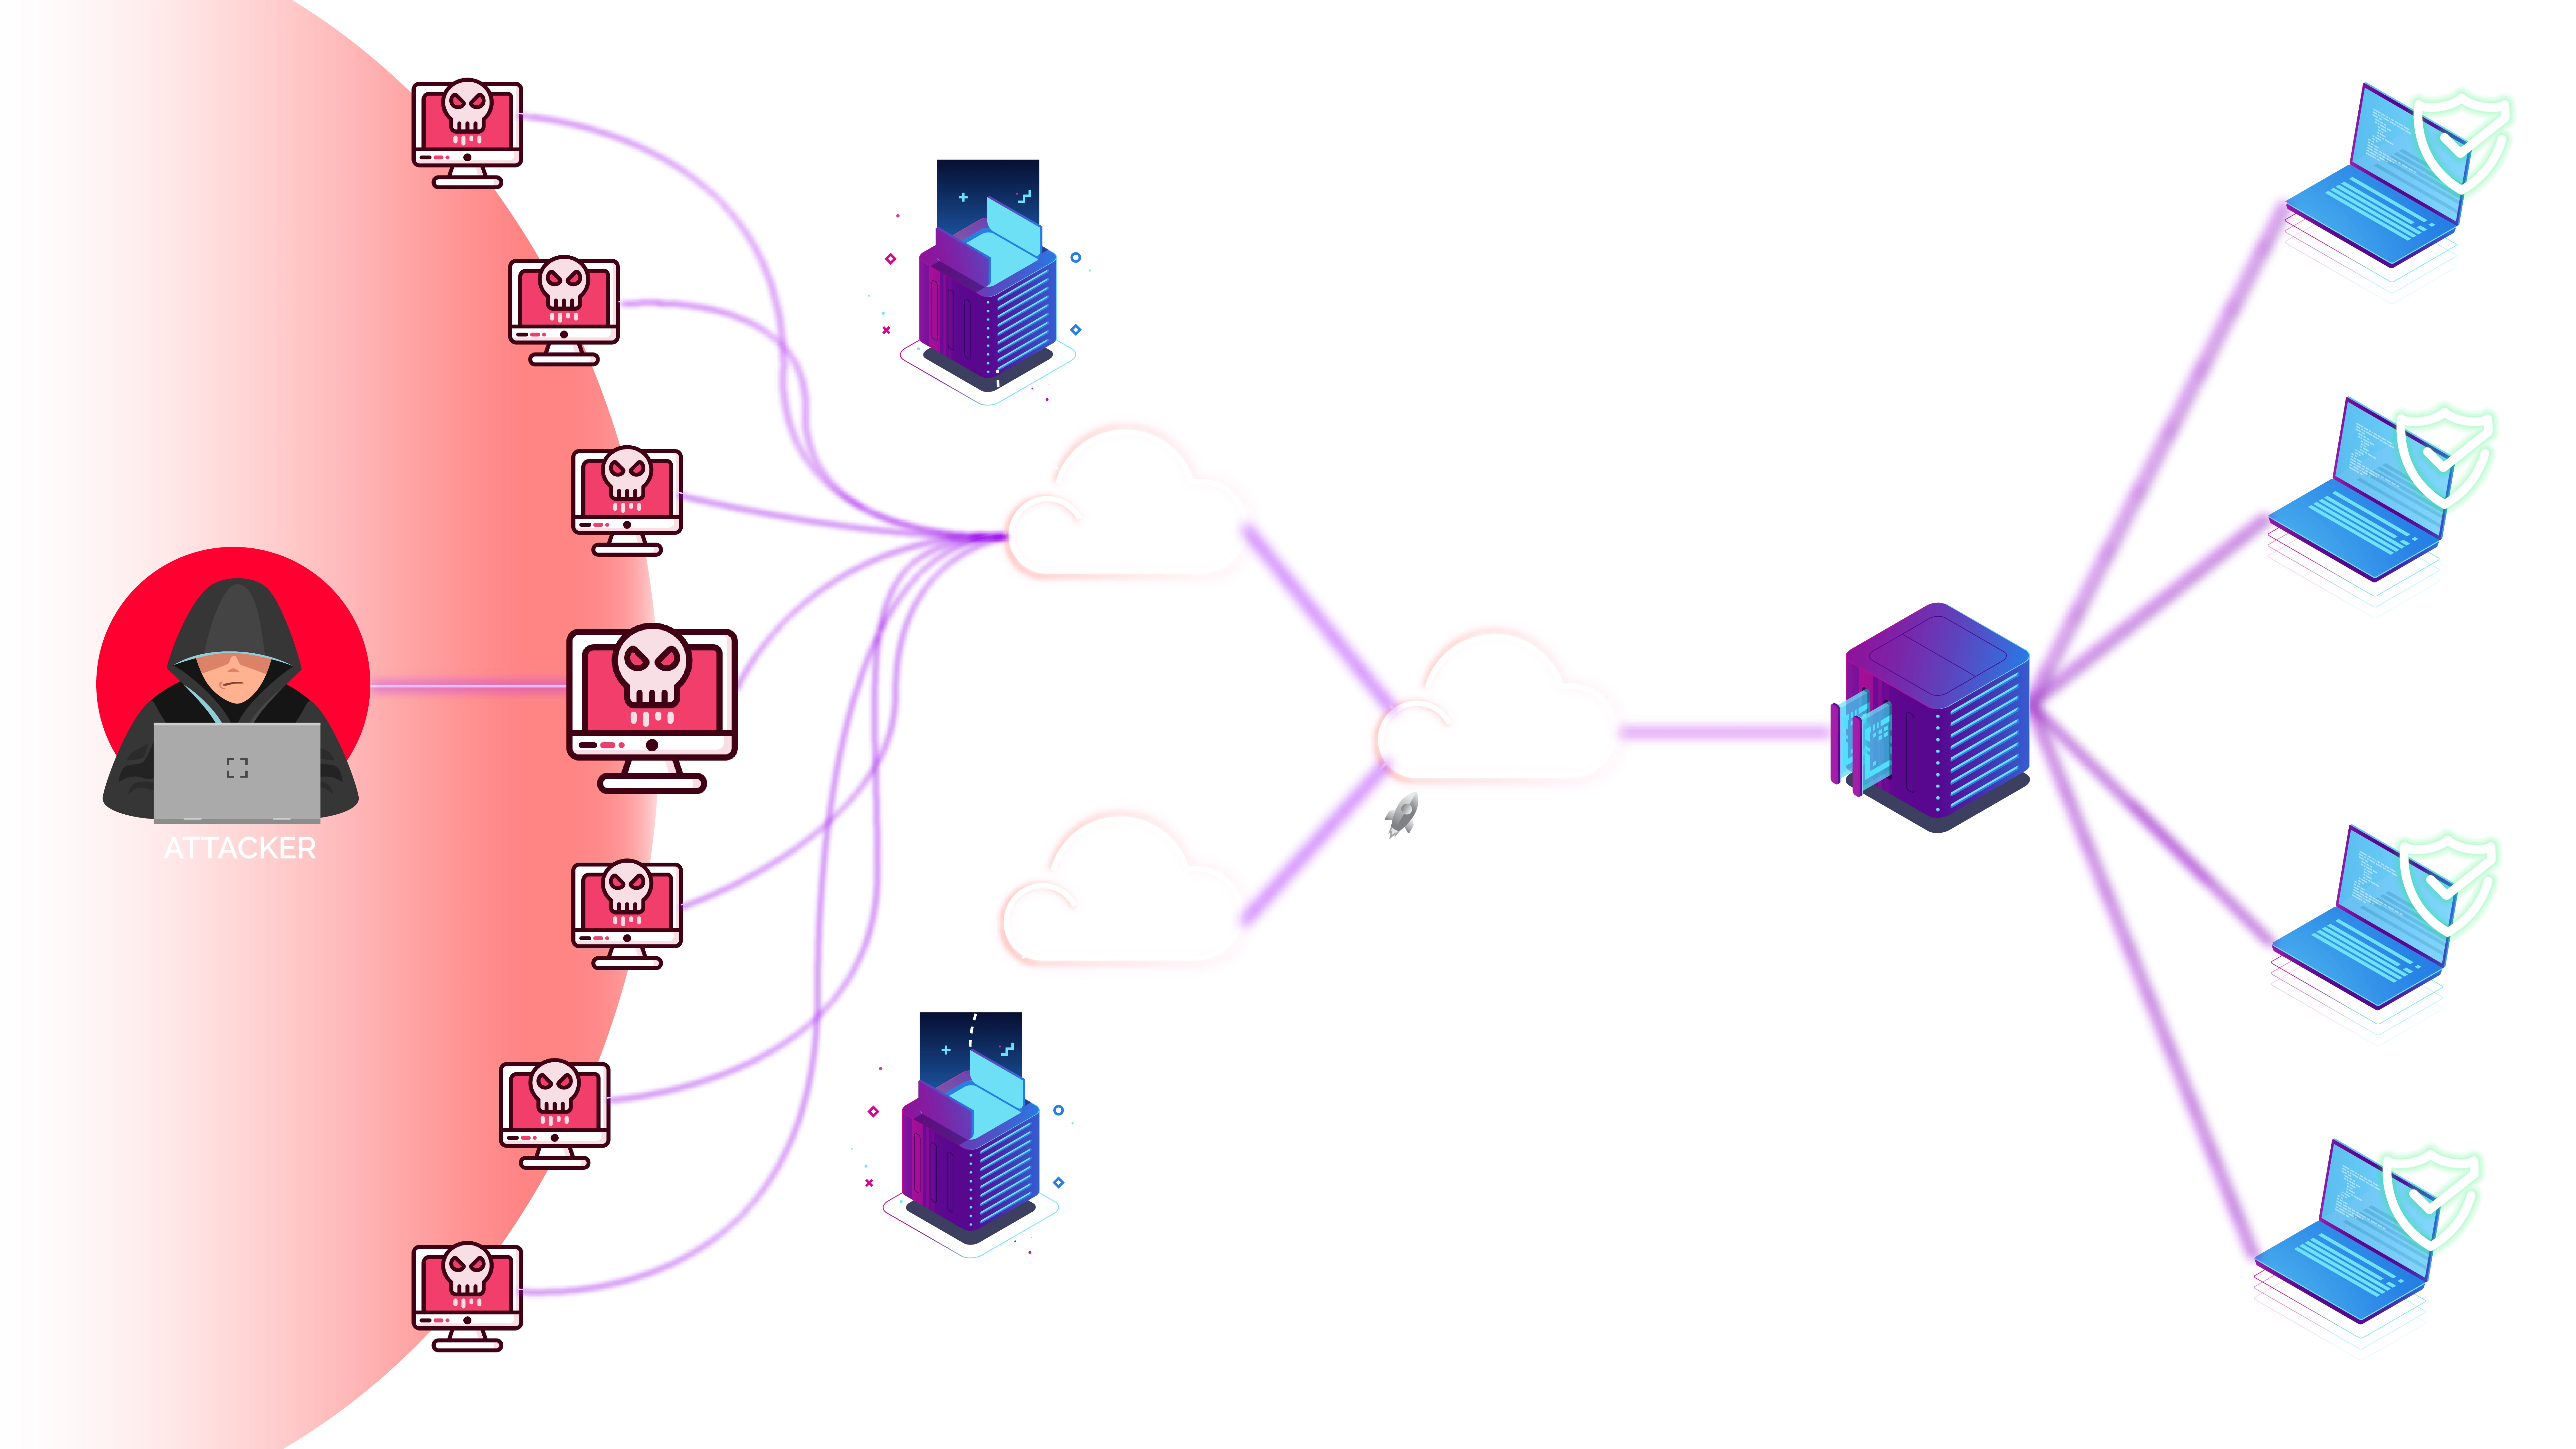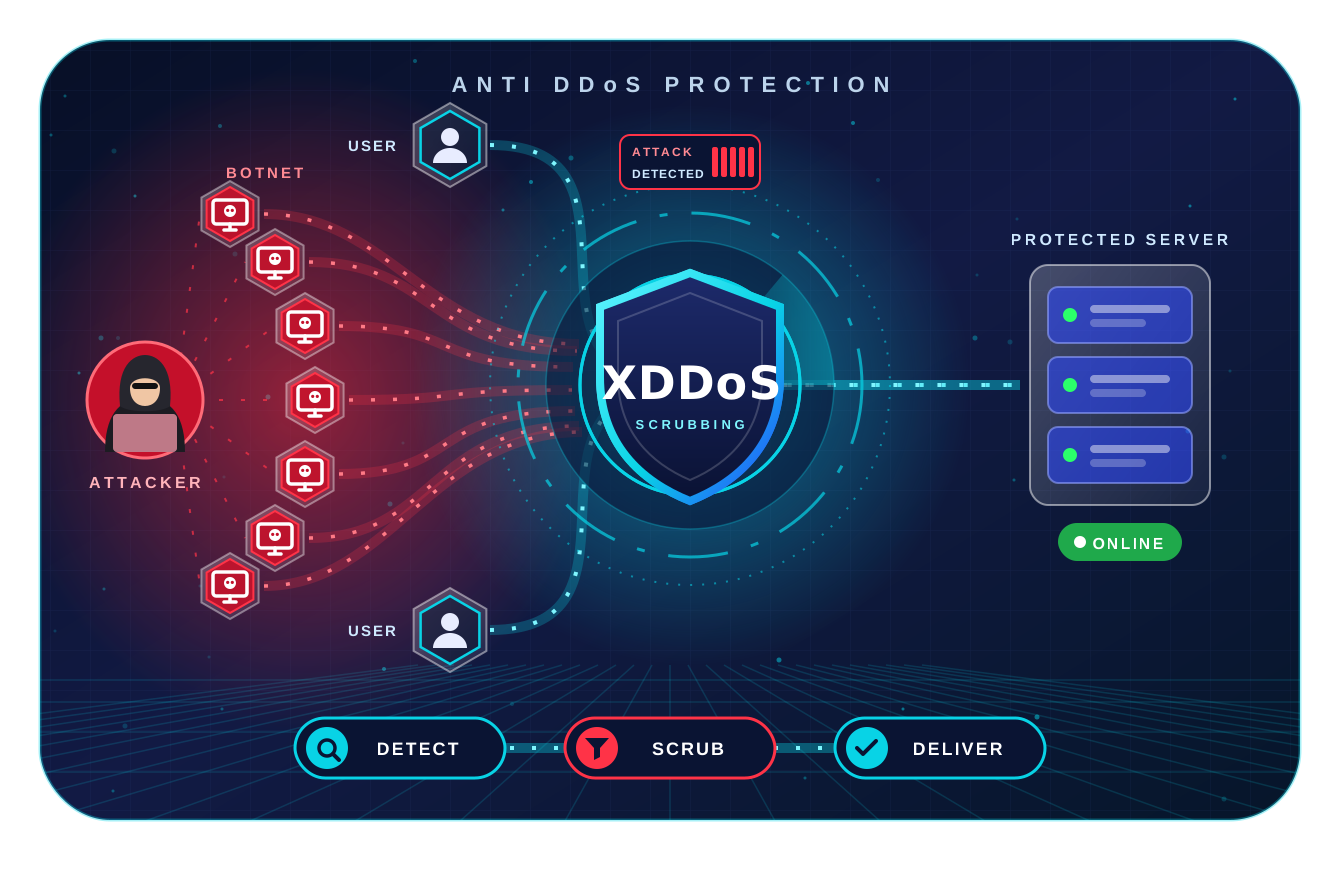
XDDoS – botnet attack traffic scrubbed while clean traffic reaches the protected server

XDDoS

Distributed Denial of Service

A malicious attempt to disrupt the normal traffic of a targeted server, service, or network by overwhelming it with a flood of internet traffic. This is achieved by using multiple compromised computer systems as sources of attack traffic. These systems can include computers and high-performance servers.

  • Bandwidth protection
  • Volumetric DDoS attack protection
  • Automatic blocking of malicious attacks
  • Managed 24/7 by Moratel SOC Team

Potential
Target of
DDoS Attack

Website

Server

Apps

Network

Email

Modern DDoS threats do not discriminate. Cybercriminals weaponize automated botnets to simultaneously strike every layer of your digital surface—paralyzing public-facing Websites, exhausting Server resources, disrupting mobile Applications, flooding core Networks, and choking corporate Email communication.

Without layered protection, a single point of failure can trigger a cascading infrastructure blackout, leading to severe financial drain, brand degradation, and operational standstills.

XDDoS Protection Architecture

Integrated workflow and traffic scrubbing mitigation system

XDDoS protection architecture infographic

Default Mitigation Rules

International

Traffic > 3 Gbps or > 400k PPS to a single destination IP & port will be dropped.

Local

Traffic > 1.5 Gbps or > 100k PPS to a single destination IP & port will be dropped.

DDoS Attack Landscape

No industry is immune. Attacks are spread across every sector—and growing fastest where services matter most.

Attack share by industry

Share of all DDoS attacks, %

  • Finance22%
  • Government sector19%
  • Telecommunications16%
  • Entertainment14%
  • Retail12%
  • Manufacturing7%
  • Logistics5%
  • Education3%
  • Others2%

Industries with highest YoY growth

Year-over-year growth in attacks, %

  • Government sector128%
  • Finance97%
  • Entertainment86%
  • Telecommunications37%
  • Retail32%
  • Manufacturing32%
  • Education12%
  • Logistics8%

Don’t let DDoS attacks impact your business and operations.

XSECURE Anti DDoS

Attack traffic is stopped upstream, before it can flood your link.

  • Bandwidth protection
  • Volumetric DDoS attack protection
  • Automatic blocking of malicious attacks
  • Managed 24/7 by MoraRepublic SOC Team
Without protection
Without protection: attack traffic floods the upstream link, the pipe becomes congested and the customer service goes down. ATTACKER ATTACKER USER IIX UPSTREAM FLOODED CONGESTED ROUTER FIREWALL CUSTOMER SERVICE DOWN
With XSECURE Anti DDoS
With XSECURE Anti DDoS: attack traffic is scrubbed in the upstream cloud and only clean traffic reaches the customer, with reports in the customer portal. ATTACKER ATTACKER USER IIX UPSTREAM ANTI DDoS TRAFFIC REPORT Customer Portal ROUTER FIREWALL CUSTOMER ONLINE

Your DDoS Report

Every attack, every mitigation—in a real-time report on the customer portal. Scroll the screen to explore a sample.

XSECURE ANTIDDOS / CUSTOMER-REDACTED CSOC

DDoS Attack Report — CUSTOMER-REDACTED

2026-10-01 00:00 GMT+7 — 2026-10-08 15:11 GMT+7 · 71 alerts shown · high importance

  • Prefix xxx.xxx.0.0/23 +11
  • Automit TMS ON
  • Automit traffic OFF
  • Blackhole auto OFF
  • Flowspec auto ON
Date rangeLast 1MLast 3MThis MonthThis Year SeverityAllLowMediumHigh
71Total alerts
4Unique targets
19.82 GbpsPeak bandwidth
4.95 MppsPeak packet rate
71Mitigated alerts (927 rules)
5m 10sAvg duration

Attack Timeline 7 days with activity

Peak BPS Alerts
07140 Gbps10 Gbps20 Gbps 01 Oct: 14 alerts, peak 19.82 Gbps03 Oct: 6 alerts, peak 2.53 Gbps04 Oct: 10 alerts, peak 2.32 Gbps05 Oct: 11 alerts, peak 2.37 Gbps06 Oct: 10 alerts, peak 2.8 Gbps07 Oct: 13 alerts, peak 3.27 Gbps08 Oct: 7 alerts, peak 4.59 Gbps 01 Oct03 Oct04 Oct05 Oct06 Oct07 Oct08 Oct

Most Targeted Hosts

  1. 1Unknown68 alerts19.82 Gbps / 4.95 Mpps
    CLDAP AmplificationIP FragmentationUDPmDNS Amplificationmemcached Amplification
  2. 2xxx.xxx.xxx.xxx1 alert13.19 Gbps / 1.38 Mpps
    IP FragmentationUDP
  3. 3xxx.xxx.xxx.xxx1 alert19.82 Gbps / 2.09 Mpps
    UDP
  4. 4xxx.xxx.xxx.xxx1 alert9.18 Gbps / 965.42 Kpps
    UDP

Attack Vector Distribution

UDP: 70 alertsIP Fragmentation: 2 alertsmDNS Amplification: 1 alertsCLDAP Amplification: 1 alertsmemcached Amplification: 1 alerts 93%UDP
  • UDP70
  • IP Fragmentation2
  • mDNS Amplification1
  • CLDAP Amplification1
  • memcached Amplification1

Attack Vector Deep Dive

Attack vectorCountAvg durationPeak BPSPeak PPSSeverityMitigation rate
UDP705m 10s19.82 Gbps4.95 Mpps27656% 100%
IP Fragmentation25m 44s13.19 Gbps1.38 Mpps1884% 100%
mDNS Amplification14m 45s546.44 Mbps743.5 Kpps27656% 100%
CLDAP Amplification15m 45s1.13 Gbps1.29 Mpps5316% 100%
memcached Amplification14m 44s5.72 Mbps501 pps143050% 100%

Protocol Breakdown

100%UDP
  • UDP100%

Packet-Size Distribution

0-50 bytes: 5.8 Mbps51-100 bytes: 0.6 Mbps101-150 bytes: 0.05 Mbps151-200 bytes: 0.03 Mbps251-300 bytes: 0.03 Mbps651-700 bytes: 0.02 Mbps751-800 bytes: 0.02 Mbps851-900 bytes: 0.02 Mbps901-950 bytes: 0.15 Mbps951-1000 bytes: 0.25 Mbps1001-1050 bytes: 0.3 Mbps1051-1100 bytes: 0.3 Mbps1101-1150 bytes: 0.8 Mbps1151-1200 bytes: 0.7 Mbps1201-1250 bytes: 0.45 Mbps1251-1300 bytes: 0.4 Mbps1301-1350 bytes: 0.35 Mbps1351-1400 bytes: 0.3 Mbps1401-1450 bytes: 0.15 Mbps1451-1500 bytes: 0.1 Mbps 0 B1500 B

Most attack traffic: tiny 0–50 byte packets (5.8 Mbps peak)

Attack Vector vs Detection Threshold

Attack vectorObserved peakThresholdOver
UDP661.3 Mbps304.4 Mbps217%
Total traffic661.3 Mbps200 Mbps331%

Top Source Prefixes

Source prefixPeak BPSAvg BPS
xxx.xxx.0.0/xx661.3 Mbps94.47 Mbps
xxx.xxx.0.0/xx98.36 Mbps14.05 Mbps
xxx.xxx.0.0/xx90.76 Mbps12.97 Mbps
xxx.xxx.0.0/xx69.79 Mbps9.97 Mbps
xxx.xxx.0.0/xx53.13 Mbps7.59 Mbps
xxx.xxx.0.0/xx43.18 Mbps6.17 Mbps

Geographic Attack Origin

Top source countries by aggregate traffic volume

  1. 1Malaysia180.52 Mbps7x
  2. 2Indonesia26.38 Mbps45x
  3. 3Bangladesh169.82 Mbps6x
  4. 4Colombia87.58 Mbps9x
  5. 5Ukraine90.47 Mbps5x
  6. 6Viet Nam43.22 Mbps9x
  7. 7Thailand46.49 Mbps2x
  8. 8Trinidad and Tobago45.56 Mbps2x
  9. 9United States10.74 Mbps10x
  10. 10Brazil12.14 Mbps7x

Source IP Intelligence

1796Unique IPs
1404Source /24 networks
20Repeat offenders

20 IPs appeared across multiple alerts

#Source IPNetworkSeenAlerts
1xxx.xxx.xxx.xxx
AS•••••
xxx.xxx.xxx.0/242929
2xxx.xxx.xxx.xxx
AS•••••
xxx.xxx.xxx.0/242929
3xxx.xxx.xxx.xxx
AS•••••
xxx.xxx.xxx.0/242727
4xxx.xxx.xxx.xxx
AS•••••
xxx.xxx.xxx.0/242626

Attack Origin Map 454 locations

Source ASN Analysis top 10 of 20

#Autonomous systemAlertsPeak BPSAvg BPSAgg. volume
1AS••••• — network masked 183 IPs5133.68 Mbps19.1 Mbps 379.88 Mbps
2AS••••• — network masked 33 IPs4226.38 Mbps11.5 Mbps 376.45 Mbps
3AS••••• — network masked 116 IPs876.62 Mbps10.95 Mbps 303.46 Mbps
4AS••••• — network masked 27 IPs352.64 Mbps7.52 Mbps 105.65 Mbps
5AS••••• — network masked 52 IPs246.49 Mbps6.64 Mbps 92.98 Mbps
6AS••••• — network masked 12 IPs245.56 Mbps6.51 Mbps 91.12 Mbps
7AS••••• — network masked 33 IPs243.22 Mbps6.17 Mbps 86.43 Mbps
8AS••••• — network masked 11 IPs233.51 Mbps4.79 Mbps 67.02 Mbps
9AS••••• — network masked 33 IPs1519.78 Mbps7.42 Mbps 61.18 Mbps
10AS••••• — network masked 29 IPs320.54 Mbps2.93 Mbps 42.72 Mbps

Network Correlation Botnet detection

15Correlated networks
1404Total /24 networks

15 networks appeared across multiple alerts — possible coordinated botnet activity

#Source networkASNAlertsThreat
1xxx.xxx.xxx.0/24AS•••••42High
2xxx.xxx.xxx.0/24AS•••••36High
3xxx.xxx.xxx.0/24AS•••••14High
4xxx.xxx.xxx.0/24AS•••••10High

Attack Hour Distribution

05:00Peak attack hour
00:0001:0002:0003:0004:0005:0006:0007:0008:0009:0010:0011:0012:0013:0014:0015:0016:0017:0018:0019:0020:0021:0022:0023:00 001223

Mitigation Effectiveness

100%Alert coverage · 71 of 71
927Total rules
927Auto (Flowspec)
0Manual / TMS

Alert Details 71 alerts

  • HighImp: HighAlert #30884792 GbpsUDP
  • HighImp: HighAlert #30877551.33 GbpsUDP
  • HighImp: HighAlert #30874654.59 GbpsUDP
  • MediumImp: HighAlert #30872571.11 GbpsUDP
  • LowImp: HighAlert #3086742233.53 MbpsUDP
  • CriticalImp: HighAlert #3086642546.44 MbpsUDP · mDNS Amplification
  • LowImp: HighAlert #3085517889.18 MbpsUDP
  • CriticalImp: HighAlert #30815871.13 GbpsUDP · CLDAP Amplification
  • CriticalImp: HighAlert #30638585.72 Mbpsmemcached Amplification
  • HighImp: HighAlert #304947713.19 GbpsUDP · IP Fragmentation

+ 61 more alerts

Key Insights & Recommendations

  • Attack pattern

    UDP was present in 99% of all alerts with peak bandwidth of 19.82 Gbps. It was the sole vector in 66 alerts and part of multi-vector attacks in 4.

  • Target analysis

    Host Unknown received 96% of all attacks (68 alerts). A dedicated mitigation policy or rate-limit may help.

  • Strong protection

    Excellent mitigation coverage at 100%. Auto-mitigation policies are effectively protecting the infrastructure.

  • Duration analysis

    Average attack duration is 5m 10s. Short durations indicate the mitigation response is effective.

  • Multi-vector attacks

    4 alerts involved multiple attack vectors simultaneously and may require layered defence.

  • Botnet correlation

    839 source /24 networks appeared across multiple alerts, with 111 high-threat networks spanning 4+ alerts.

  • Attack timing

    Peak attack activity observed at 05:00. Align SOC staffing and monitoring with observed attack patterns.

© 2026 MoraRepublic · Sample report · customer data masked

01 Oct: 14 alerts03 Oct: 6 alerts04 Oct: 10 alerts05 Oct: 11 alerts06 Oct: 10 alerts07 Oct: 13 alerts08 Oct: 7 alerts01030405060708
71Alerts detected · 7 days
020
19.82 GbpsPeak attack
100%Alerts mitigated · 71 of 71
Auto927 Manual0
927Auto mitigation rules

Anti DDoS Features

Clean-pipe protection for your network, backed by a service you can see.

Protection

  • Safeguard against Volumetric Attacks

    Protect Content Service Providers (CSP) and downstream customers from L3–L4 DDoS attacks using the best mitigation methods.

  • Surgical Mitigation

    Automatically eliminate traffic caused by attacks without reducing or interrupting valid traffic.

  • Clean Pipe As-A-Service

    Clean Pipe as-a-service for CSP and downstream customers.

  • Flow Data Analysis Capability

    A multi-layer detection engine analyzes traffic and detects traffic anomalies.

Service

  • 24/7 Customer Service Support

    Round-the-clock support and customer service.

  • Technical Features

    Clean-pipe Anti-DDoS solution for IPv4 mitigation, using NetFlow-based detection over TCP/IP (ISO Layer 3 & Layer 4).

  • Mitigation within 15 minutes

    From the moment an attack is detected, traffic is diverted to the mitigation system within 15 minutes.

  • Incident Reports

    Monthly incident reports on request, plus a web-based dashboard showing your network traffic in real time.

Why Anti DDoS by MoraRepublic

Continuous monitoring, automatic mitigation and full transparency.

  1. 01

    Monitoring & Detection

    The MoraRepublic SOC monitors network traffic continuously, using DDoS protection to detect malicious attacks.

  2. 02

    Response & Mitigation

    Thresholds are set from your bandwidth or packets per second (PPS). When an attack on a specific IP and port exceeds them, the system automatically mitigates traffic to that IP and port.

  3. 03

    Reporting

    DDoS reports are available in the customer portal.