XDR – Extended Detection and Response

XDR

Extended Detection & Response

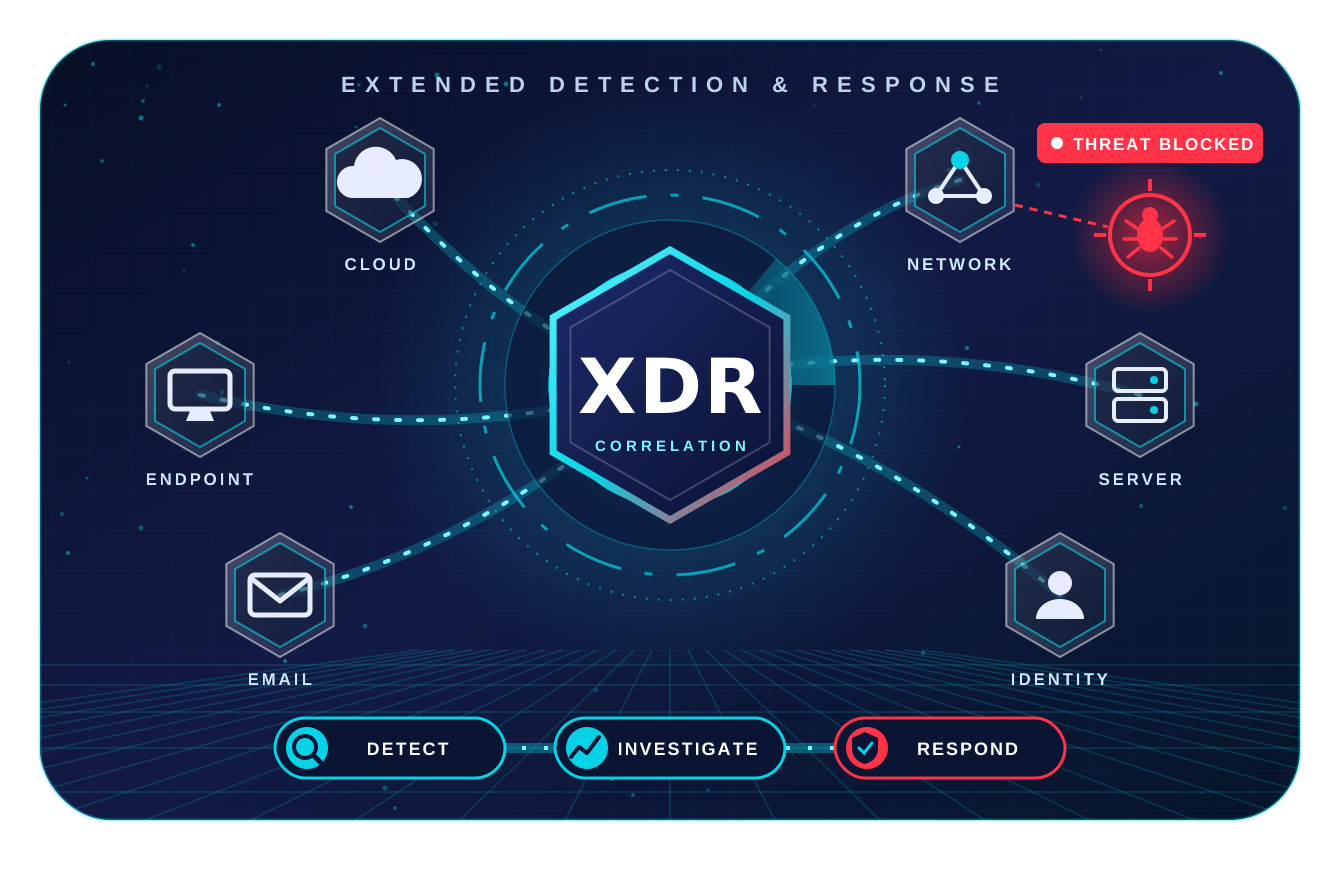
Extended Detection and Response (XDR) is an advanced cybersecurity platform that consolidates and correlates data from diverse security layers—including endpoints, networks, cloud environments, and applications—to deliver holistic threat detection, investigation, and response capabilities.

  • Unified visibility across endpoints, network & cloud
  • Automated threat detection & correlation
  • Rapid investigation and response
  • Managed 24/7 by Moratel SOC Team

XSECURE XDR

One platform that sees, correlates and acts across your entire infrastructure.

Laptop protected by a security shield

Extended Detection and Response (XDR) is an advanced cybersecurity platform that consolidates and correlates data from diverse security layers—including endpoints, networks, cloud environments, and applications—to deliver holistic threat detection, investigation, and response capabilities.

  • Multi Source Integration

    Collect data from multiple sources and consolidate it in one platform for comprehensive analysis.

  • Automatic Detect & Response

    Using analytics, AI & ML, XDR automatically detects threats and responds quickly, often with automated actions.

  • Analytics & Correlation

    In-depth analysis that correlates data from multiple sources to detect complex threat patterns and attacks that traditional security solutions may miss.

  • Operational Simplification

    Combining multiple security tools into one platform lets security teams work more efficiently and effectively.

XDR Transformation

How endpoint security evolved into extended detection and response.

  1. 1990 – 2000

    Traditional Antivirus

  2. 2000 – 2010

    Behavioral Detection Antimalware

  3. 2010

    Endpoint Detection & Response (EDR)

  4. 2018 – Now

    Extended Detection & Response (XDR)

XDR Features

Visibility, speed and automation working together.

  • Data Collection & Better Visibility

    Collect data from multiple data sources across the entire IT infrastructure (e.g. endpoints, network and cloud), for wider visibility of threats.

  • Fast Intrusion Detection

    Analyze data from multiple sources to detect potential security risks quickly and accurately.

  • Automatic Response

    Use automation to respond to security threats quickly and reduce mitigation time.

How XDR Stops a Threat

From the first malicious process to expert follow-up by our CISM team.

Malware

  • Ransomware
  • Bots
  • Trojan Horse
  • Worms
  • Virus
  • Backdoor

Agent Endpoint

  1. Automate Kill Process Malware01
  2. Quarantine02
  3. Delete Malware Related Files03

XDR Cloud

24/7 CISM Team

  • Threat Hunting
  • Vulnerability Assessment

Better than EDR

XDR extends protection far beyond the endpoint.

Aspect EDR XDR
Coverage Endpoint only Endpoint, network, cloud, email
Visibility Limited to endpoint Covers the entire infrastructure
Threat Complexity Focused on endpoint threats Detects multi-vector threats
Integration No integration Integrates across security solutions
Data Analytics Only from endpoint Data from various sources

Why XDR by MoraRepublic

Technology backed by people, around the clock.

  • Monitoring

  • Detection

  • Response

MoraRepublic SOC Team will carry out mitigation for every incident captured by XDR.