XWAF – Web Application Firewall blocking malicious web traffic

XWAF

Web Application Firewall

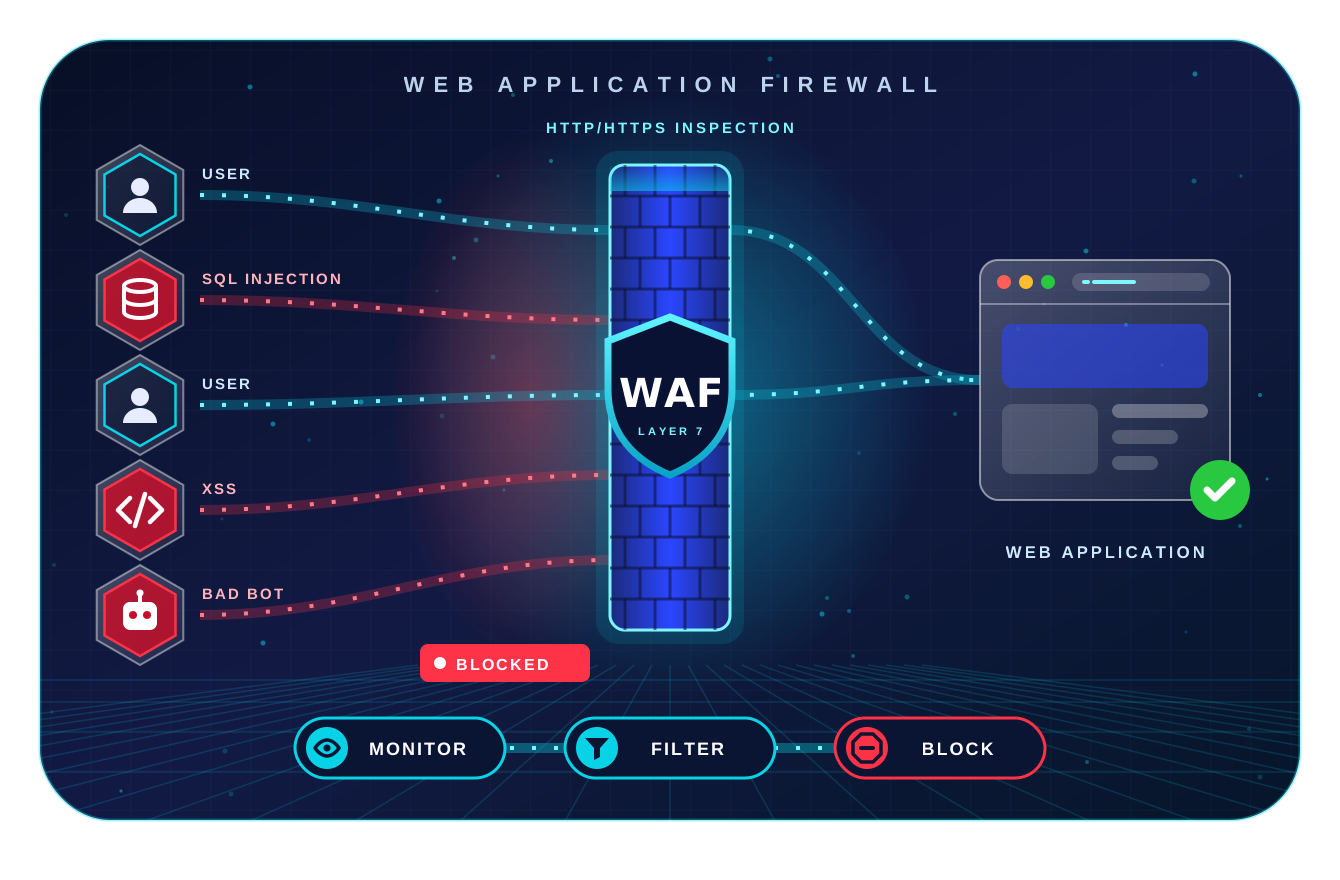
A security solution designed to monitor, filter, and block malicious traffic targeting web applications. It acts as a protective barrier between the web application and the internet, defending against common threats such as SQL injection, cross-site scripting (XSS), and other application-layer attacks.

  • SQL injection & XSS protection
  • Layer 7 DDoS protection
  • Bot mitigation & vulnerability scanning
  • Managed 24/7 by MoraRepublic SOC Team

XSECURE WAF

A protective barrier between your web application and the internet.

Isometric firewall protecting servers and applications
  • Monitor

    Analyzes HTTP/HTTPS traffic to your web applications in real time.

  • Filter

    Separates legitimate visitors from malicious requests before they reach your application.

  • Block

    Stops attacks at the edge, ensuring the security, integrity, and availability of your web applications.

Common threats stopped

  • SQL Injection
  • Cross-Site Scripting (XSS)
  • Application-Layer Attacks

WAF Features

A Web Application Firewall (WAF) monitors and filters web traffic to detect and prevent attacks such as SQL injection, cross-site scripting (XSS), and other web application layer threats.

  • DDoS Protection (Layer 7)

    Protection against DDoS attacks aimed at disrupting the availability of web applications by flooding servers with malicious traffic.

  • Bot Mitigation

    Safeguards web applications from malicious bot activities, including data scraping, information theft, and fraudulent account creation.

  • Vulnerability Scanning

    Provides automated scanning of web applications to identify and address potential security vulnerabilities.

How Traffic Flows

Every request passes through layered protection. Legitimate users reach your apps; malicious requests are stopped at the WAF.

User

Malicious Request

  1. DDoS Protection

  2. DC Firewall

  3. HTTP/SSL Inspection

  4. WAF

  5. Load Balancer

  6. Web Apps

  • Legitimate request — delivered
  • Malicious request — blocked at the WAF